Phishing
A message, under control.
Offsecure builds phishing exercises by hand. The message, the page, and the technique are made for this organization, rather than taken from an automated catalog. The result is who acted, and what that action would have given up.
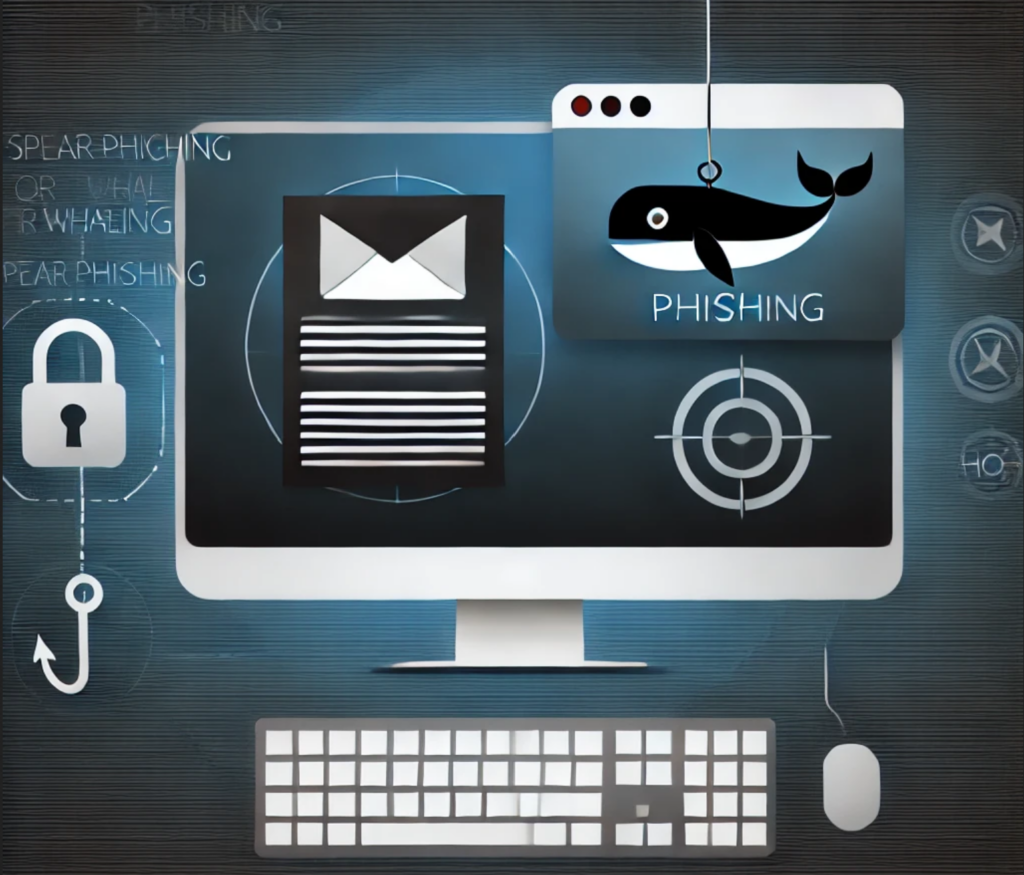
Phishing remains one of the attacks that depends on a person. The simulation finds that exposure before an attacker does, then leaves training and a further exercise so the same miss is not repeated.
Only amateurs attack machines; professionals target people.
Bruce Schneier
What the exercise is
Spear phishing aimed at named people, or a broader email campaign. Both are written for the industry and the organization in front of the test.
Realistic
Campaigns follow the shape of a real attack, including the message a specific person would receive. The point is the gap an attacker would use.
Measured
The report counts who clicked, who submitted something sensitive, and who reported the message, with the training that follows from those numbers.
Repeated
Training and remediation come after the exercise, and a later exercise measures whether the same action still happens.
The standards it can sit under
The service can be aligned to CBEST, TIBER, GDPR, PCI-DSS, and NIST, where the organization is held to them.
The campaigns are handcrafted, including the exploits and the infrastructure behind them. That is a different test from a plug-and-play campaign bought from a vendor.
How it runs
- Consultation. The organization, the risk, and the objective are agreed first.
- Design. Emails and pages are built for this environment and for the vectors that apply to it.
- The launch. The campaign goes to the people in scope, as a real phishing message would.
- The report. Behavior and the weaknesses the exercise exposed, written so they can be acted on.
- Training. The material the team needs in order to recognize the next one.