Red teaming
Elite adversary simulation.
Offsecure runs covert adversary simulation as a specialist service, designed to test how your security holds up against a realistic, objective-led attack. Each engagement is built around a specific outcome you want to protect, with operators following the paths a real adversary might take — through people, exposed services or compromised credentials, and onward through lateral movement and privilege escalation towards the target. The defensive team remains unaware of the exercise, while a designated white team maintains oversight, manages the rules of engagement and ensures the operation stays within agreed boundaries. The result is a clear view of whether the objective could be reached, how effectively your controls detected and responded to the activity, and where meaningful improvements can be made.
A red team engagement is a controlled cyberattack designed to test an organization’s ability to withstand a real-world adversary. An independent team is given a defined objective and pursues it by following an attacker’s path: gaining initial access, moving through the environment, and achieving the access or action required to meet its objective. The defenders encounter the operation as they would a genuine intrusion, without necessarily knowing it is a test. A designated white team, established in advance, oversees the engagement, maintains awareness of its boundaries, and retains the authority to stop it. Within those agreed limits, the attack is conducted using real-world adversarial techniques to evaluate the organization’s defenses, detection capabilities, and response.
Why it is needed
Companies need red teaming because it is the most realistic way to go through a controlled cyberattack. It has the shape of an intrusion, and it remains an exercise: an objective and limits agreed before the start.
Regulation
A supervisor, a board, or a regime is often the reason the test is asked for. That may be freestyle, or it may sit with CBEST or TIBER-EU.
A shared picture
The business and the security team can discuss one attack on their own organization, rather than risk in the abstract.
On their terms
The attack happens as an exercise, with a white team the organization appoints, rather than as an incident nobody chose.
Red teams are established by an enterprise to challenge aspects of that very enterprise’s plans, programs, assumptions, etc. It is this aspect of deliberate challenge that distinguishes red teaming from other management tools.
U.S. Department of Defense
How it is performed
01
Objective
Named with the white team before any action. One outcome, the rules, and what is out of bounds.
02
Access
A person, an exposed service, or a credential. No courtesy foothold, unless the objective requires one.
03
Execution
Movement, privilege, and the objective. Quiet enough that the response is the one an intrusion would draw.
04
Close
It stops at the objective, at a safety rule, or when the white team ends it. The path is then written in the order it happened.
How it is delivered
A booked engagement, bounded before it starts, and independent of the team under test. Offsecure works for the white team.
- Covert. Defenders are not informed. They meet the activity with the process they actually have.
- White team. A small group you appoint. They can see the work and stop it.
- One objective. Named in advance. The engagement is finished against that outcome, not against a quota of findings.
- Freestyle. One objective and a set of rules. No prescribed playbook.
- CBEST. Intelligence-led testing in the pattern used for financial services in the United Kingdom.
- TIBER-EU. Intelligence-led, with white-team control built into the exercise.

The team
A red team manager, a red team operator, and a project manager. Other specialists come in only if the path needs them. That may be AWS, Azure, Active Directory, Kubernetes, or whatever the engagement turns toward.
How long it runs
The length is flexible, unless a regulation sets it. Otherwise the engagement goes until the objective, a safety rule, or the white team calls a stop. It is not padded to fill a calendar.
What is delivered
At the end, the path is written in the order it happened, and whether the objective was reached. With that, what was seen along the way, and where the engagement stopped.
What the result is judged on
An engagement is scored on the objective. Not on a count of weaknesses.
Reached
Whether the objective was reached, or the path was stopped.
Time
From the first foothold to the objective.
Seen
Which detections fired, which stayed quiet, and how late the ones that fired were.
Closed
The control that would have ended the path. Named, not implied.
Focused services
The same practice, taken one phase at a time. Each can be booked on its own.
Threat intelligence
What an attacker can already see. People, domains, and exposed services, gathered before an objective is chosen. It can stand alone, or it can decide where a red team engagement begins.
Phishing
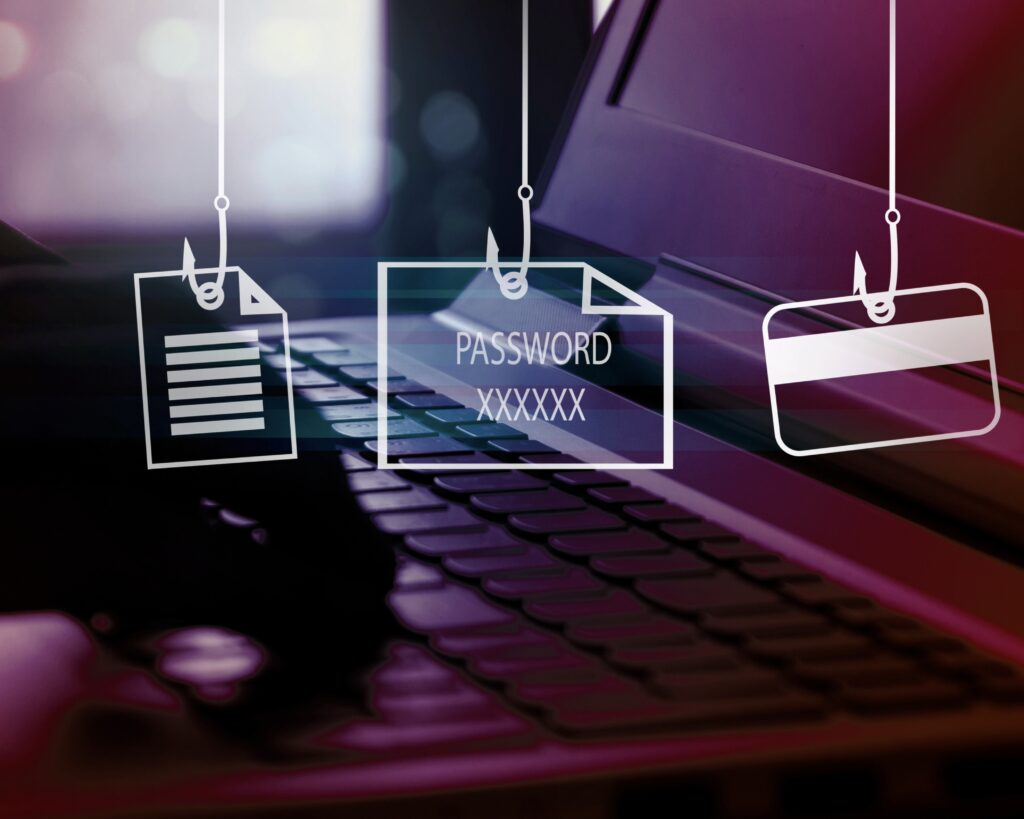
A message built for this organization, sent under control. The measure is who acts on it, and what that action would have handed an attacker.
Purple teaming
The security team stays on a channel for the exercise. Techniques are reported as they run, and detection comes back on that same line.